Showing posts with label passwordcracking. Show all posts

Tuesday, 23 June 2015

How To Change Windows password wihout knowing current password

Hello guys, you know that User and Administrator password in widows are protecting your computer from any unauthorized access. So that chooses a strong password and safe your computer or system files from unauthorized access. But  if you forget your windows login password, or  want to change your password without knowing current or old password ,then don�t worry , In this we are telling about  to  change windows login password with a some simple method, which you can do easily perform.  

Method -1 

Step-1  Select �My computer� and press Right click on it and chose a �Manage� options. or Press Windows+R Key and type compmgmt.msc in Run Box and hit enter.

Step-2 "Computer Management windows" will open, and Select System Tools from Right window pane and after that Go to "Local Users and Groups" and double click on it.

Step-3 Now Click on "Users" and you will see all the login accounts of  your computer. And after that select your account.

Step-4 After selecting your login Account press Right Click on it. And then choose "Set Password" option.After that one pop-up box will open and click on "Proceed".

Step-5 Enter the New Password and conform them, then click on "OK" Button.

Step-6 Now your login Password has been successfully changed .you can restart your system and check with your new password. 

Method -2

Change password with "Command Prompt"

Step-1 Firstly go to windows start menu and type "cmd" in search box . Then select cmd and Run as Administrator.

Step-2  After that  type below command in cmd  

  net user %username% EthicalHackingTricks
         you can change "EthicalHackingTricks"  to with your choice password and after that hit enter.

Now your password have been successfully changed . and enjoy !!
Read more...

Thursday, 11 June 2015

62.5 Million Zomato Users Hacked By Hackers 2015


The online restaurant and search service that provides food place near you, home delivery,dining outs and night life of many cities in India and in other 21 countries, hacked by hacker with a single simple API vulnerability in it and hacker also explaining the way they hack into Zomato database and have access to 62.5 millions users details.
This hack was because of the vulnerability that was there in zomato that leads to database hack and the security researcher Anand Prakash found vulnerability in zomato. And he done a simple API call in the browser_id and gain access to the database of Zomato. He had explain the whole step he done to hack zomato database and gaining access to millions details.
As creating account in zomato needs you phone number, addresses, date of birth, link Instagram account and some more. Now all these details got hacked by hackers and millions user�s details are now exposed.


Read more...

Tuesday, 9 June 2015

WhatsApp Accounts Can Be Easily Hijacked 2015


An important warning for those of you who use the popular mobile messaging app WhatsApp: Your account may not be as secure as you think it is. A recent article from The Hacker News explains that someone can easily hijack your WhatsApp account if they gain physical access to your phone, even if just for a few moments. Theoretically, the attack could be used against any of the 800 million current WhatsApp users.
The actual mechanism of the attack isn�t sophisticated, and it doesn�t require any hacking skill at all. To start, a thief sets up a WhatsApp account on a new phone using your account�s phone number. During this process, a confirmation code will be sent to your phone. If the thief can intercept your phone during this time, they can enter it on their version of WhatsApp, stealing your account. Simply locking your phone isn�t enough protection against the attack, since the thief can simply request the code be called in.
Because a thief needs to be in physical possession of your phone, your WhatsApp account is likely safe from Chinese hackers located halfway across the globe. It�s not safe, however, from a nosy snoop at work or a jealous boyfriend. That�s where the real danger here is � someone close to you may want to spy on you, monitoring your WhatsApp messages and browsing through your contacts.
WhatsApp will hopefully fix this particular issue with its authentication protocol, given how news of the hijacking vulnerability has spread. In the meantime, there�s no reason to be high alert, but you should aim to be more physically protective of your device in general. Don�t leave your phone out on your desk at work unattended, and keep it in your pocket or stashed away when you have guests visiting your home. And be careful of who you lend your device to if you think they may have an interest in spying on your messages.
Read more...

Wednesday, 3 June 2015

Microsoft Plans to Add Secure Shell (SSH) to Windows

Until now Unix and Linux system administrators have to download a third-party SSH client software like Putty on their Windows machines to securely manage their machines and servers remotely through Secure Shell protocol or Shell Session (better known as SSH).


This might have always been an awkward feature of Windows platform, as it lacks both � a native SSH client software for connecting to Linux machines, and an SSH server to support inbound connections from Linux machines. But�

Believe it or not:


You don't need to deal with any third-party SSH client now, as Microsoft is working on supporting OpenSSH.
Yes, Microsoft has finally decided to bring OpenSSH client and server to Windows.

The PowerShell team at Microsoft has announced that the company is going to support and contribute to OpenSSH community in an effort to deliver better SSH support in the PowerShell and Windows SSH software solutions.

So, the upcoming version of Windows PowerShell � the command-line shell and scripting language � will allow users to manage Windows and Linux computers through SSH.
"A popular request the PowerShell team has received is to use Secure Shell protocol and Shell session (aka SSH) to interoperate between Windows and Linux � both Linux connecting to and managing Windows via SSH and, vice versa, Windows connecting to and managing Linux via SSH," explained Angel Calvo, PowerShell Team Group Software Engineering Manager.
"Thus, the combination of PowerShell and SSH will deliver a robust and secure solution to automate and to remotely manage Linux and Windows systems."
For those who are unaware, SSH is basically designed to offer the best security when accessing another computer remotely. It not only encrypts the remote session, but also provides better authentication facilities, with features like secure file transferring and network port forwarding.

This is not first time Microsoft has planned to adopt SSH for its Windows platform, the company had tried to allow the secure shell protocol to be used within Windows twice but was unable to implement it.

However, developers who are eager to use this new functionality in PowerShell still have to wait for some time, as the project is still in the early planning phase. So far, there isn�t any definite release date.!!
Read more...

Monday, 18 May 2015

FBI: Banned Security Researcher Admitted to Hacking Plane In-Flight !!

A security researcher who was pulled out from a United Airlines flight last month had previously admitted to Federal Bureau of Investigation (FBI) that he had taken control of an airplane and made it fly briefly sideways.


Chris Roberts, the founder of One World Labs, was recently detained, questioned and had his equipment taken by federal agents after he landed on a United flight from Chicago to Syracuse, New York following his tweet suggesting he might hack into the plane's in-flight entertainment system.
In that particular tweet, Roberts joked: "Find me on a 737/800, lets see Box-IFE-ICE-SATCOM, ? Shall we start playing with EICAS messages? 'PASS OXYGEN ON' Anyone? :)"
The federal agents addressed the tweet immediately and took it seriously following the Roberts� capabilities of such hacking tactics.

In the FBI affidavit first made public Friday - first obtained by APTN National News - Roberts told the FBI earlier this year about not once, but repeatedly hacking into aircrafts' in-flight entertainment (IFE) systems while on board.
"During these conversations, Mr. Roberts stated ... he had exploited [flaws] with IFE systems on aircraft while in flight. He compromised the IFE systems approximately 15 to 20 times during the period 2011 through 2014," FBI Special Agent Mark Hurley wrote in his application. "He last exploited an IFE system during the middle of 2014."

How the researcher made this possible?


The documents claim that Roberts connected his laptop to the plane�s IFE system via a modified Ethernet cable, allowing him to access other airplane systems.

During at least one instance, Roberts reportedly claimed to have overwritten the code on the airplane's Thrust Management Computer while aboard a flight and successfully controlled the system to issue the climb command.
By issuing the �CLB� or climb command, Roberts "caused one of the airplane engines to climb resulting in a lateral or sideways movement of the plane," according to the FBI warrant application.

No Systems were Harmed:


Roberts claimed via Twitter that no systems were harmed during the trip. Moreover, Roberts told Wired in an interview that the FBI has taken his remarks about hacking "out of context" of their discussions with the agency.

Roberts claimed that he had only watched data traffic on airplanes, and he has only attempted the hack in a simulated environment because he believed that such hack attacks were possible.

"It would appear from what I�ve seen that the federal guys took one paragraph out of a lot of discussions and a lot of meetings and notes and just chose that one as opposed to plenty of others," he said, declining to elaborate further.

Since this incident, United Airlines has launched a bug bounty program inviting security researchers and bug hunters to report vulnerabilities in its websites, apps and web portals.

Roberts has neither been arrested by the FBI nor charged with any crime.

Source :- TheHackerNews
Read more...

Friday, 15 May 2015

Venom Vulnerability Exposes Most Data Centers to Cyber Attacks 2015 !

After a new security vulnerability surfaced Wednesday, many tech outlets started comparing it with HeartBleed, the serious security glitch uncovered last year that rendered communications with many well-known web services insecure, potentially exposing Millions of plain-text passwords.

But don�t panic. Though the recent vulnerability has a more terrific name than HeartBleed, it is not going to cause as much danger as HeartBleed did.

Dubbed VENOM, stands for Virtualized Environment Neglected Operations Manipulation, is a virtual machine security flaw uncovered by security firm CrowdStrike that could expose most of the data centers to malware attacks, but in theory.
Yes, the risk of Venom vulnerability is theoretical as there is no real-time exploitation seen yet, while, on the other hand, last year�s HeartBleed bug was practically exploited by hackers unknown number of times, leading to the theft of critical personal information.

Now let�s know more about Venom:


Venom (CVE-2015-3456) resides in the virtual floppy drive code used by a several number of computer virtualization platforms that if exploited�

...could allow an attacker to escape from a guest 'virtual machine' (VM) and gain full control of the operating system hosting them, as well as any other guest VMs running on the same host machine.

According to CrowdStrike, this roughly decade-old bug was discovered in the open-source virtualization package QEMU, affecting its Virtual Floppy Disk Controller (FDC) that is being used in many modern virtualization platforms and appliances, including Xen, KVM, Oracle's VirtualBox, and the native QEMU client.

Jason Geffner, a senior security researcher at CrowdStrike who discovered the flaw, warned that the vulnerability affects all the versions of QEMU dated back to 2004, when the virtual floppy controller was introduced at the very first.

However, Geffner also added that so far, there is no known exploit that could successfully exploit the vulnerability. Venom is critical and disturbing enough to be considered a high-priority bug.

Successful exploitation of Venom required:


For successful exploitation, an attacker sitting on the guest virtual machine would need sufficient permissions to get access to the floppy disk controller I/O ports.

When considering on Linux guest machine, an attacker would need to have either root access or elevated privilege. However on Windows guest, practically anyone would have sufficient permissions to access the FDC.

However, comparing Venom with Heartbleed is something of no comparison. Where HeartBleed allowed hackers to probe Millions of systems, Venom bug simply would not be exploitable at the same scale.

Flaws like Venom are typically used in a highly targeted attack such as corporate espionage, cyber warfare or other targeted attacks of these kinds.

Did venom poison Clouds Services?


Potentially more concerning are most of the large cloud providers, including Amazon, Oracle, Citrix, and Rackspace, which rely heavily on QEMU-based virtualization are vulnerable to Venom.

However, the good news is that most of them have resolved the issue, assuring that their customers needn't worry.
"There is no risk to AWS customer data or instances," Amazon Web Services said in a statement.
Rackspace also said the flaw does affect a portion of its Cloud Servers, but assured its customers that it has "applied the appropriate patch to our infrastructure and are working with customers to remediate fully this vulnerability."

Azure cloud service by Microsoft, on the other hand, uses its homemade virtualization hypervisor technology, and, therefore, its customers are not affected by Venom bug.

Meanwhile, Google also assured that its Cloud Service Platform does not use the vulnerable software, thus was never vulnerable to Venom.

Patch Now! Prevent yourself


Both Xen and QEMU have rolled out patches for Venom. If you're running an earlier version of Xen or QEMU, upgrade and apply the patch.

Note: All versions of Red Hat Enterprise Linux, which includes QEMU, are vulnerable to Venom. Red Hat recommend its users to update their system using the commands, "yum update" or "yum update qemu-kvm."

Once done, you must "power off" all your guests Virtual Machines for the update to take place, and then restart it to be on the safer side. But remember, only restarting without power off the guest operating system is not enough for the administrators because it would still use the old QEMU binary.
Read more...

Tuesday, 5 May 2015

London Railway System Passwords Exposed During TV Documentary 2015 !!

The Weakest Link In the Information Security Chain is still � Humans.

And this news has ability to prove this fact Right.

One of London's busiest railway stations has unwittingly exposed their system credentials during a BBC documentary. The sensitive credentials printed and attached to the top of a station controller's monitor were aired on Wednesday night on BBC.


What could be even worse?

If you think that the credentials might have been shown off in the documentary for a while or some seconds, then you are still unaware of the limit of their stupidity.

The login credentials were visible for about 44 minute in the BBC documentary "Nick and Margaret: The Trouble with Our Trains" on Wednesday night, which featured Nick Hewer and Margaret Mountford � the two business experts, both famous for their supporting role on The Apprentice.

The documentary was available on the YouTube, but have now been removed due to security concerns.

While talking about the concerns of the British railway network, the duo walked into London Waterloo's control room where these sensitive credentials were seen stuck to a monitor of a system.

A screenshot of the offending monitor with the machine-produced login was captured and shown above. The screenshot points to a particular workstation signaller's control desk seems to be running a type of software that controls signals and trains over? the final approach to Waterloo station?.

Now this is going to be a great idea to keep passwords. Isn�t this? I mean if it is, then what�s the need of putting passwords for the devices if you stuck it on the top of that device.

This shows that we are just humans. Remembering so many personal passwords of our different online accounts and then to remember the passwords of others � Ahh! Quite a tough Job.

Okay, now let�s come to another security concern. What would you expect next?

Password3, Wow! Isn�t this great password?


I mean, at least keep a strong password that take some time to guess and crack. Password3 could be in the list of top ten weakest passwords.

The incident occur few days after the news came that the computer systems controlling the railway signalling system in the United Kingdom could potentially be hacked by cyber criminals to cause incoming trains to crash into one another at highest speeds.

However, this security blunder of revealing passwords mistakenly in an interview, video or news channel is not new at all.

Last year, the World Cup security centre�s internal Wi-Fi passwords for the FIFA World Cup 2014 were broadcast live. Also, French TV network TV5Monde failed to keep its passwords secret and revealed a collection of the TV station�s usernames and passwords live on TV!!

Keep Connected !!  
Like On Facebook !!

Read more...

Friday, 1 May 2015

Famous Online Indian Portal �Rediff� Hacked By Palestinian Hacker 2015

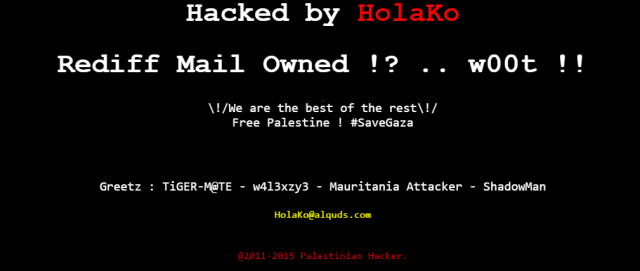
On 30th April, 2015, a Palestinian-friendly hacker going with the online handle of HolaKo hacked and defaced a subdomain of Rediff.com, a famous Indian news, information, shopping and entertainment web portal.

The targeted domain (businessemail.rediff.com) belongs to Rediff enterprise providing emails, Windows andLinux web hosting services in India.
In an exclusive conversation with HolaKo, HackRead was told that reason for targeting Rediff was to deliver a message about Israeli occupation of Palestinianland.
The deface message was left in following words: 
HACKED BY HOLAKO, REDIFF MAIL OWNED!? W00T !! WE ARE THE BEST OF THE REST. FREE PALESTINE ! #SAVEGAZA
A full preview of the deface page is available below:
subdomain-of-indian-online-portal-rediff-hacked-by-palestinian-hacker
Link of targeted domain along with its zone-h mirror as a proof of hack is available below:
 I THINK THEY FOUND OUT I AM IN THEIR SERVER 
HolaKo claims he had access to Rediff�s databases, emails and login data, but the access was cutoff by site admin later on. 
In past the hacker was in news for defacing Institute of Electrical and Electronics Engineers (IEEE,org) website in support of Palestine. You can contact the hacker here.{AT YUOUR OWN RISK}
At the time of publishing this article, the targeted Rediff domain was restored and accessible online. 
Read more...

Website and Twitter account of high-tech automaker HACKED by Tesla

The website and Twitter account of high-tech automaker Tesla were hacked over the weekend as part of a prank by angry rival hackers. Tesla CEO Elon Musk�s personal twitter account was also hacked around Saturday night (US Standard Time).


The first sign of hijacking was noticed around 1:52 p.m., when the company�s Twitter account had a tweet that declared it being under the control of attackers and the name changed from �Tesla Motors� to  �#RIPPRGANG�. The tweet posted on the carmaker�s account said, �This Twitter is now run [sic] by Henry Blair Strater [sic] from Oswego Illinois, call me at [number redacted]�. 

A few minutes later, the account began promising free Teslas to those who followed certain accounts or to those who called a certain phone number. The number belonged to a repair shop in Illinois which was flooded with calls.

Nearly at that time, Tesla�s website was hacked by the same attackers. Visitors were redirected to a website with ISIS in the URL, a Laden-ranting video and a picture of a man resembling Osama Bin Laden.
(PC-google images)

The Twitter account war restored around 2:45 p.m., an hour after it was uncompromised and the website was back to its usual state at around 6:30 p.m.
Elon Musk�s Twitter account was hijacked by miscreants who claimed to be from the infamous Lizard Squad Hacking crew, known as Autismsquad.
Read more...

Monday, 27 April 2015

9 years old cybersecurity expert hacks Android smartphone in minutes 2015

9-year-old cybersecurity expert hacks Android smartphone in minutes


Wondering how secure your Android smartphone is? Well, a 9-year-old cybersecurity expert has demonstrated how hackers could steal contacts, call logs and messages within just 15 minutes.


Speaking at the Security B-sides Conference last week, Harmony School of Science third-grader Reuben Paul took to the stage to promote safer smartphone security. His Keynote speech stressed the importance of being extra careful when downloading apps, showing how even seemingly safe software can be used by cybercriminals to access sensitive data and snoop on your location.
�If a child can do it then a regular hacker can do it� so I just want everybody to be aware [and to] be more careful when you download games and stuff like that,� he said.
Paul is a rising star of the computer security industry, speaking at a number of other conferences as well as acting as CEO of Prudent Games; a company which attempts to teach people about threats through educational apps. The company�s games includeCracker Proof, which teaches good password practice, and Crack Me If you Can, which teaches all about brute force attacks.
Read more...

Monday, 6 April 2015

UBER Accounts hacked and sell for only $1 dollar 2015


UBER has become popular for getting a taxi, private car or any other vehicle for the worldwide move by a simple mobile application. Though, the head-quarter of UBER is in San Francisco, California, but the service is spread over fifty-five countries and more than two hundred cities. It has become more popular both to riders and drivers for a convenient move around the city. Day by day the users and the popularity is increasing of UBER for its easy service. With the increasing fame, it has attracted the hacker attention. Unfortunately, it is now prey to the hacker and its fame is in a danger now.

The very lowest rate 1USD is enough now to get an activated UBER account to enjoy the facilities to move around the city free of cost. Two vendors on AlphaBay are responsible for this terrible hacking. They are selling the active accounts along with the username and password for only $1!!! All information about payment is provided on a file to the purchaser.
Another breaking news is that, the purchaser can also get some extra information with an active account. Such as partial credit card data, email address, trip history, phone number, home and office location etc.
They are selling the accounts over AlphaBay market by giving some attractive and grabbing title like �n UBER ACCOUNT � WORLDWIDE TAXI, anyone can buy a UBER account anonymously.� Another hacker is giving the same offer in $5 with lifetime validity period and the discount offer in case of the bulk purchase. They have included it on their product list with such appealing title. One of the two hackers has said that, they have sold more than hundred UBER accounts to different buyers.
But news to be worried is that, even now it is not clear about their stolen source. Till now it is sure that, UBER security system is hacked or the worst that can be, the UBER authority has compromised with the hackers. Surprisingly, UBER has denied about the hacking and they have declared that, no evidence is found in the investigation and they have reported it to the low authority.
UBER advised about careful sharing and login to the users. UBER said to avoid same login from on multiple online sites and recommended the users to give unique and strong password to their account for security purpose. UBER also advised, not to re-use the same username and password to multiple sites.
*******************Thanks For Your Support********************
*****************Ethical Hacking News**************************
Read more...

Thursday, 2 April 2015

How Hackers Could Delete Any YouTube Video With Just One Click!

A security researcher has discovered a simple but critical vulnerability in Google-owned YouTube that could be exploited by anyone to knock down the whole business of the popular video sharing website.

Ethical Hacking News


Kamil Hismatullin, a Russian security bod, found a simple logical vulnerability that allowed him to delete any video from YouTube in one shot.

While looking for Cross-Site Scripting (XSS) or Cross-Site Request Forgery (CSRF) flaws in YouTube Creator Studio, Hismatullin came across a simple logical bug that could wipe up any video by just sending an identity number of any video in a post request against any session token.

The bug was simple but critical as it could be exploited by an attacker to fool YouTube easily into deleting any video on its system.
"I've fought the urge to [delete] Bieber's channel," Hismatullin wrote in his blog post. "Luckily no Bieber videos were harmed."
Citing the consequences of the issue, Hismatullin said "this vulnerability could create utter havoc in a matter of minutes in [attackers'] hands who could extort people or [just] disrupt YouTube by deleting massive amounts of videos in a very short period of time."
The researcher reported the bug to Google, and the search engine giant fixed the issue within several hours. Hismatullin won $5,000 cash reward from Google for finding and reporting the critical issue and an extra $1337 under the company�s pre-emptive vulnerability payment scheme.

Over a month ago, a similar bug was reported in Facebook's own systems that could have exploited by attackers to delete any photo from anyone�s Facebook account. However, the social networking giant fixed the relatively simple issue.


Read more...